Researcher details Wi-Fi flaw affecting Broadcom-based routers
Quentin Kaiser estimates that about 1.5 million devices in Belgium are vulnerable; his incomplete list also includes router models sold worldwide.
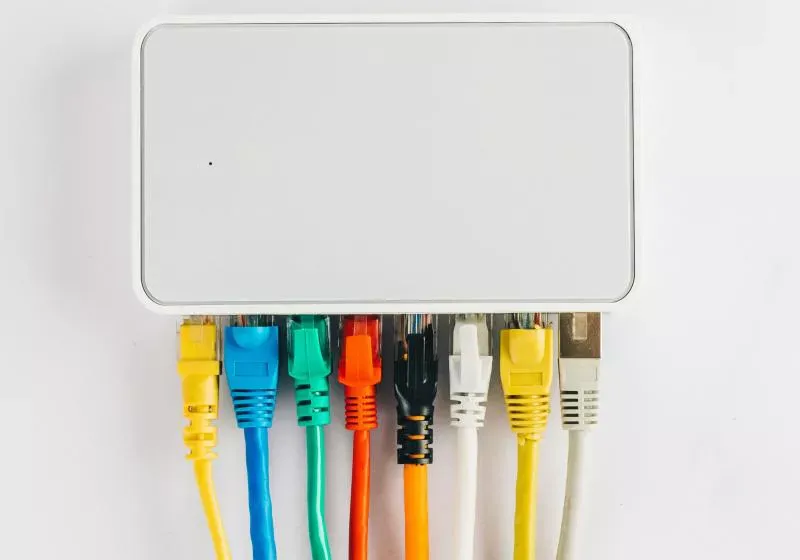
Security researcher Quentin Kaiser has disclosed a vulnerability in older Broadcom router software that allows nearby attackers to extract data from memory or execute code without knowing the Wi-Fi password. Presenting his findings during Hexacon in Paris on October 16, Kaiser estimated that about 1.5 million devices in Belgium were vulnerable.
Kaiser named the flaw WPSplinter. It affects Broadcom's implementation of WPS, a feature for connecting devices through a button press rather than a password. Mishandling of certain message exchanges enables the attack before pairing is completed. The vulnerability concerns Broadcom's software implementation, rather than the WPS protocol itself.
In one demonstration, Kaiser extracted a Wi-Fi key from an Askey TCG3000 gateway provided by Orange Belgium, received it wirelessly and used it to connect. He also obtained a remote shell over Wi-Fi on a Sagemcom-made Proximus BBOX3V+, without needing an internet connection on his side.
Kaiser confirmed the vulnerability in gateways supplied by Proximus, Orange and VOO, representing three of Belgium's four major internet service providers. His incomplete inventory of affected equipment also names Cisco, TP-Link, Netgear, Sagemcom, Nokia, ZTE and Zyxel. Devices using the same Broadcom chips are sold internationally.
After Kaiser reported the issue in July, Broadcom said it had been aware of it since 2018 and had replaced the older WPS software. It directed him to device manufacturers and declined to seek a CVE identifier, saying the code was obsolete and no longer supported. Kaiser disputed the completeness of the 2018 patch and argued that the missing identifier likely prevented warnings from reaching manufacturers and providers.