OpenCode breach affects 1.4% of Console users
Keys for external AI services may have been exposed, and some users have reported charges they did not authorize.
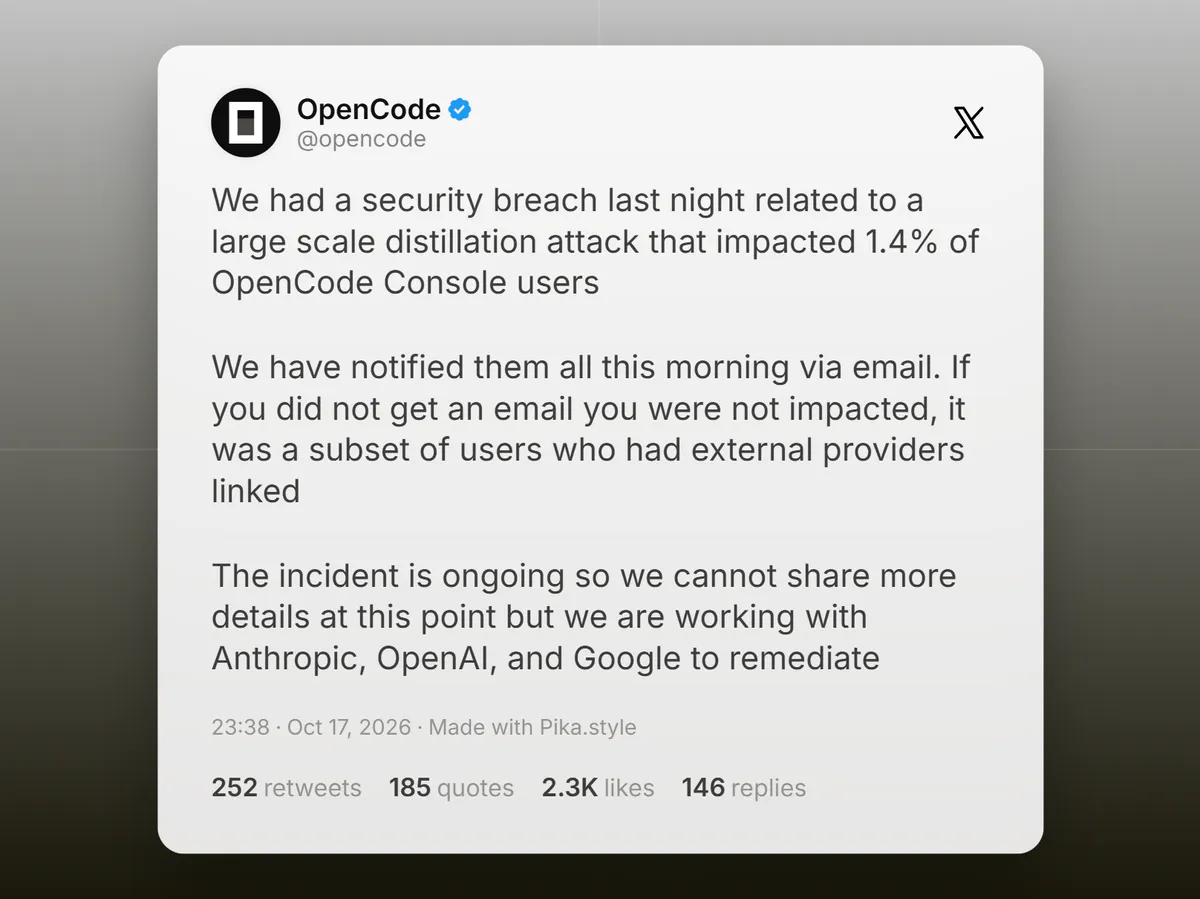
OpenCode has disclosed a breach affecting 1.4% of users of its Console, with credentials for connected AI providers potentially exposed. The company described the incident as ongoing and said Anthropic, OpenAI and Google were helping it respond.
An email warning from OpenCode attributed the intrusion to an older system that was being retired. Credentials potentially compromised included workspace keys for Anthropic and OpenAI. OpenCode is an open-source coding tool that allows developers to connect different providers’ models using their own API keys.
On Reddit, one user alleged that an Anthropic account incurred $400 in unauthorized charges. Another reported around €200 in Google usage charges and a project suspension for excessive abuse. A separate commenter said alerts about OpenAI and Anthropic usage preceded OpenCode’s notification.
According to OpenCode, only some accounts connected to external providers were affected. It said all impacted users had received an email and that anyone without a notification was unaffected. Its instructions to affected users included replacing and revoking provider credentials, updating applications that rely on them, and checking usage records for unfamiliar activity.
OpenCode associated the intrusion with a large-scale distillation attack, in which outputs collected from one AI model are used to train another.